# Manage Access Keys
Tigris access keys authenticate programmatic access to your object storage buckets. You can manage them via the Tigris Dashboard or programmatically using the AWS CLI.
## Create an Access Key[](#create-an-access-key "Direct link to Create an Access Key")
### From the Dashboard[](#from-the-dashboard "Direct link to From the Dashboard")
1. **Open the Dashboard**
Go to the [Tigris Dashboard](https://console.storage.dev) and select **Access Keys** from the sidebar.
2. **Click "Create New Access Key +"**
Optionally choose your service endpoint (`Default` or `Fly`).
3. **Fill in Key Details**
* **Key Name**: e.g., `ci-access`, `backup-script`
* **Permissions**:
* **Admin** – full access (dev use only)
* **Editor** – read/write and bucket administration for selected buckets
* **ReadWrite** – read/write to selected buckets without bucket administration
* **ReadOnly** – read-only for selected buckets
See [default allowed operations](#default-allowed-operations) for what a `standard` key can do without a bucket role.
4. **Click Create**
You’ll receive:
* Access Key ID
* Secret Access Key *(shown once—store it securely)*
* S3 & IAM endpoint URLs
* Region
Set the following environment variables:
```
export AWS_ACCESS_KEY_ID=your-access-key-id
export AWS_SECRET_ACCESS_KEY=your-secret-access-key
export AWS_ENDPOINT_URL_S3=https://t3.storage.dev
export AWS_ENDPOINT_URL_IAM=https://iam.storage.dev
export AWS_REGION=auto
```
### Programmatically[](#programmatically "Direct link to Programmatically")
1. **Set Environment Variables**
```
export AWS_ACCESS_KEY_ID=tid_
export AWS_SECRET_ACCESS_KEY=tsec_
export AWS_ENDPOINT_URL_S3=https://t3.storage.dev
export AWS_ENDPOINT_URL_IAM=https://iam.storage.dev
export AWS_REGION=auto
```
2. **Create an Access Key**
```
aws iam create-access-key --endpoint-url "$AWS_ENDPOINT_URL_IAM"
```
The new key uses the `standard` scope.
## Default allowed operations[](#default-allowed-operations "Direct link to Default allowed operations")
A new access key uses the `standard` scope unless you create it with `no_default_allow`. A standard key can perform these operations in the organization even if you assign no bucket role and attach no IAM policy. You can turn this default off for an existing key. See [Change the default allowed operations](#change-the-default-allowed-operations).
It can `CreateBucket` and `ListBuckets` (all buckets in the organization). It can `CreateAccessKey`. It can `ListAccessKeys`, `UpdateAccessKey`, and `DeleteAccessKey` only for keys it created. Organization admins can manage all keys.
It can `CreatePolicy`. It can list, get, delete, and attach only policies it created, and only to keys it created (`ListPolicies`, `GetPolicy`, `GetPolicyVersion`, `DeletePolicy`, `AttachUserPolicy`, `DetachUserPolicy`, `ListUserPolicies`, `GetUserPolicy`, `ListEntitiesForPolicy`). Organization admins can manage all policies.
The policy document can use any [supported S3 action](/docs/iam/policies/supported-actions/.md), including wildcards such as `s3:Get*` or `s3:*`. Each `Resource` must be an S3 ARN. The bucket name in the ARN cannot contain `*`. Object prefixes such as `arn:aws:s3:::my-bucket/uploads/*` are allowed. The key must own every bucket named in the policy. A key cannot create a policy that grants access to a bucket it does not own. This limit does not apply to organization admins.
## Change the default allowed operations[](#change-the-default-allowed-operations "Direct link to Change the default allowed operations")
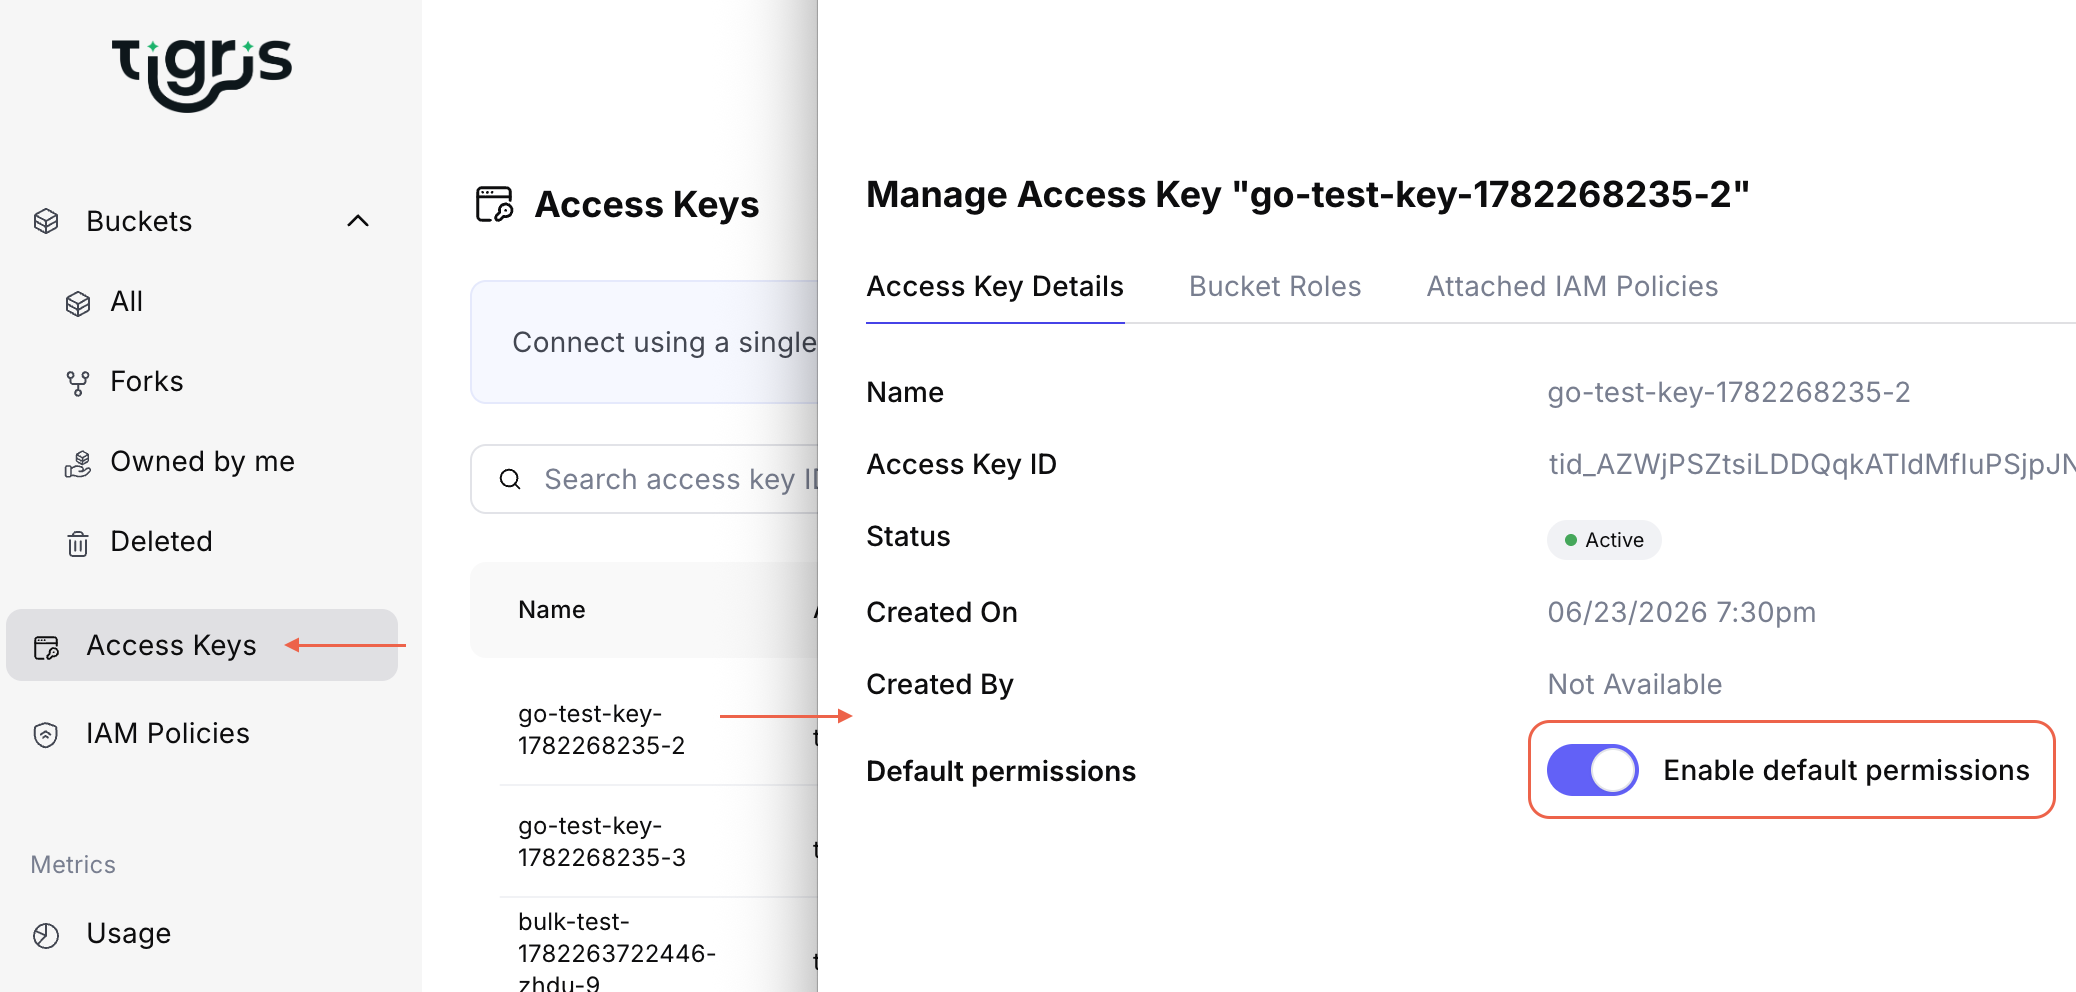
A key that you create in the Dashboard always uses the `standard` scope. You can turn the default allowed operations off after you create the key.
1. **Open the Dashboard**
Go to the [Tigris Dashboard](https://console.storage.dev) and select **Access Keys** from the sidebar.
2. **Open the Key Details**
In the list, click the access key that you want to change.
3. **Set the Default Allowed Operations**
Turn the **Default allowed operations** toggle off. The key now uses the `no_default_allow` scope. It can do only what its bucket role and its attached IAM policies allow. To go back to the `standard` scope, turn the toggle on.
## Delete an Access Key[](#delete-an-access-key "Direct link to Delete an Access Key")
### From the Dashboard[](#from-the-dashboard-1 "Direct link to From the Dashboard")
1. **Open the Dashboard**
Go to the [Tigris Dashboard](https://console.storage.dev) and select **Access Keys**.
2. **Find the Key**
In the list, locate the access key you want to delete.
3. **Delete the Key**
Click the 🗑️ icon next to the key. A confirmation modal will appear—click **Delete** to confirm.
### Programmatically[](#programmatically-1 "Direct link to Programmatically")
Ensure your environment variables are still set (see above), then run:
```
aws iam delete-access-key --endpoint-url "$AWS_ENDPOINT_URL_IAM" --access-key-id=tid_
```
> 🔐 Tip: Rotate or delete unused access keys regularly.